Step One: Leveraging Cloudflare’s Enormous Global Footprint supplemented by Google Cloud Resources
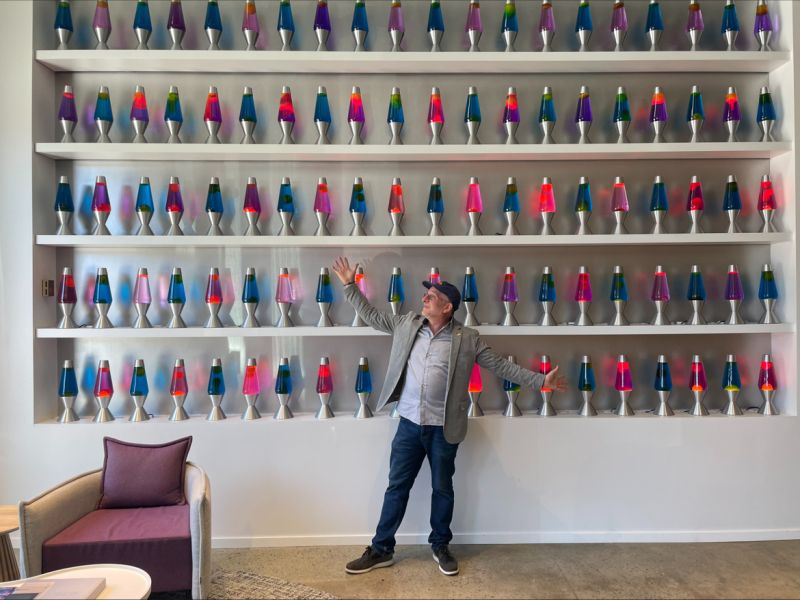
Cloudflare is well-known for its threat mitigation capabilities, especially in dealing with DDoS attacks. Cryptography enthusiasts also recognize Cloudflare for its “entropy wall” at their headquarters, a fascinating showcase of their commitment to randomness in security.
Cloudflare’s entropy wall is a bookshelf filled with lava lamps. While it may seem like a bit of security theater, the lava lamps’ slow deformation and non-linear motion provide true randomness that traditional computation cannot produce, as traditional systems are deterministic and any random number generated is pseudo-random.
Browsing their blog here, and this video about the entropy wall here should give you some more of an idea of the role this plays. For those playing at home the way your computer encrypts your data is using algorithms that take into account the minor movements of your mouse, or fluctuations in heat, or orientation of your phone. From combinations of these truly random actions you end up with a “private:public” key pair in which asymmetrical encryption is made possible. I am simplifying because the current standard employed by any end-end messaging service that uses encryption is a derivation of the ‘Signal Protocol’ originally developed by the previously (boooo!) open-sourced Signal.
Modern encryption uses a stack of algorithms and cryptographic techniques to produce truly secure encryption (until the government forces you to put in a backdoor.) It doesn’t matter how strong your front door is then.
Cloudflare’s Product Expansion
Cloudflare has expanded its product offerings to include traditional protection methods, ZeroTrust mechanisms, and serverless application modules called “Workers.” For the Orion AI Threat Intelligence project, Cloudflare’s global coverage is essential. Workers can detect threats using parameters defined by a KV store and controlled by another worker. AI Workers can even perform inference.
With just a few lines of TypeScript or Rust code, we can build entire services. Combined with the Pages service, you get a full-stack app with scale, reliability, and a serverless architecture to supplement the rest of your architecture with an emphasis on security.
What Are Workers?
Cloudflare Workers provide a serverless execution environment that allows you to create new applications or augment existing ones without configuring or maintaining infrastructure. They enable exceptional performance, reliability, and scale. Something this random dude in the Southern part of the planet can even dream of achieving. Wink wink, nudge nudge Cloudflare.
Orion’s Use Cases (So Far)
- Threat Hunters Deployed as Individual Workers: While it’s unclear if we can spin up various workers at individual endpoints of the user, this is important for the Orion Network nodes to scan within relevant CIDR ranges. Orion plans to continuously collect threat data from diverse sources, particularly SMBs, due to the risks associated with new technology.
- KV Service: The KV Service is a dynamic key-value store used to identify different parameters for different Threat Hunters.
- AI Workers: Deploying inference models like Mistral-7B at the edge for low-resource-intensive operations.
- Internal Functions: Leveraging zero trust architecture, live caching, and AI Gateway (integrated with Portkey-AI) to control the flow of data through the 100+ models in Portkey.
This is far from an exhaustive list and if admitted into the startup program or funded/find a co founder we will use far more. The same goes for Google Cloud (GCP).
Paired Deployment with Google Cloud Platform
Cloudflare’s serverless, reliable, and globally available functions are invaluable for isolating or mitigating threats. Some functionalities, however, are best handled by Google Cloud Platform (GCP), supported by the Google AI Startup program. This includes:
- GCP VPC for secure networking.
- GCP Cloud Storage, BigQuery, and MongoDB for data storage.
- GCP Cloud Functions and Cloud Run for scalable compute.
- Google Kubernetes Engine (GKE) for container orchestration.
- GCP Pub/Sub and Dataflow for data streaming and processing.
- GCP IAM for access control and security.
- ELK stack on GCP: As per a previous post this is a well known, scalable observability stack for applications.
Why This is Useful
Integrating Cloudflare’s global threat mitigation capabilities with GCP’s robust data storage and processing infrastructure allows for a comprehensive, scalable, and secure deployment. This synergy enhances Orion’s ability to detect and respond to threats efficiently while leveraging the strengths of both platforms.
The Cloudflare deployment has been accompanied by an application to their startups program and an inclusion in their “Cloudflare Workers Launchpad” program investor pool of 50+ VC’s focused on Worker use. Discussions with the CTO of Cloudflare International directed me to the product team. Though we still claim insanity, the technical and engineering efforts are becoming clearer, and the architecture more defined.
These are long days, and it’s a relentless process, but the same skills that applied in the mountain are the same here. Your mindset will give out before your body so get comfortable with being uncomfortable. Plus, this is FUN and the progress is rewarding. If you are interested in this space, please reach out!
:: Snyata
 Aylex Riom
